NEWS
ShinyHunters Hit the FBI Jobs Site Over a Warning
ShinyHunters says it stole FBI staff and applicant files from the jobs portal and will sit on them for a week if the bureau retracts its May warning.

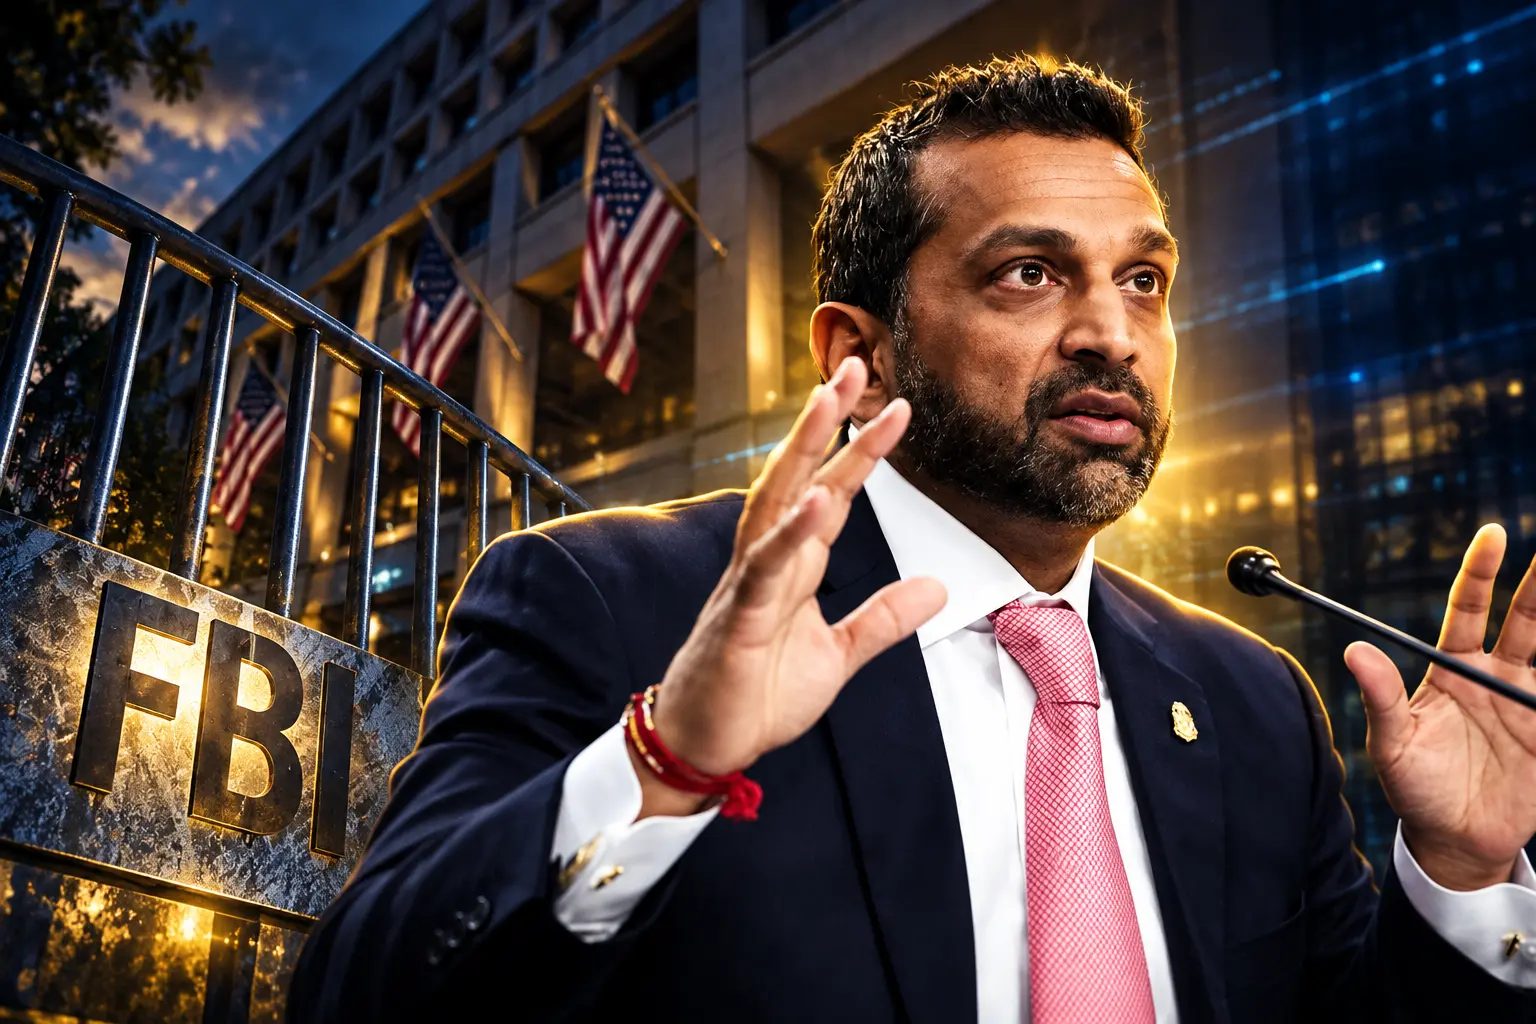
ShinyHunters says it stole personal files on FBI staff and applicants and will sit on them for a week if the bureau takes down a May warning. The group defaced apply.fbijobs.gov on September 22 and told Director Kash Patel the hit was payback, not a ransom.
The FBI says it is investigating a claimed compromise of FBIJobs.gov and alleged harm to employee personal information. It has not confirmed how much data left, who took it, or whether the break-in started at a vendor or inside the bureau.
ShinyHunters Wants the FBI Warning Rewritten
The leak-site post was addressed to Patel and Brett Leatherman, assistant director of the FBI Cyber Division. It opened like a correction notice. The group said a second-quarter “FLASH report” made “substantial false allegations,” left it “severely offended,” and failed to disrupt its work.
The public document it is quoting is not a FLASH. It is a Public Service Announcement issued May 15 after ShinyHunters claimed a cyberattack on a learning platform used by schools. The group copied three sentences from that warning, denied each one, and gave the bureau one week to correct or remove it.
As a big believer and supporter of the U.S. Constitution, we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.
ShinyHunters, leak-site post to Kash Patel and Brett Leatherman
The same post still reads like the group’s corporate notes. It tells the FBI to “make the right decision” and “don’t be the next headline,” then closes with “Thank you for your attention to this matter.” In an email, a representative added that the aim was “to solely set the record straight.”
Cynthia Kaiser, senior vice president at Halcyon’s ransomware research center, said the group “appears to be actively trying to put a target on their back.” Analysts at Flashpoint, which tracks extortion crews, have already treated a leak as the likely end of this path, money or no money. Going after home addresses of federal agents is also a way to guarantee a long manhunt, which is a strange trade for a wording change on a public warning.
The Jobs Site That Invites Strangers In
Anyone who opened the special agent application portal on September 22 saw a fake seizure notice instead of a hiring form. The banner said the site had been seized by ShinyHunters and added “rooting your systems since ’19.” By later that day the parody page was gone.
Apply.fbijobs.gov then showed a maintenance line, “We’re sniffing out site updates for you!” The main FBI Jobs page returned a 503 error. A banner on the eligibility page said apply.fbijobs.gov and the Special Agent Application Portal were unavailable and told applicants with urgent scheduling problems to write their Applicant Coordinator.
A hiring portal has to be reachable by strangers. That is the point of it. People who want to be agents, analysts, or professional staff create profiles, upload forms, and wait. ShinyHunters says that open door was enough, and that a PeopleSoft flaw on the recruitment stack led into other FBI-managed systems, including infrastructure it placed in AWS GovCloud. Oracle and Amazon have not commented. The FBI still says the point of breach is undetermined.
An FBI spokesperson said the bureau is “actively and aggressively investigating this matter” and working with the third-party providers that support FBIJobs.gov “to mitigate any and all risk.” That sentence leaves the vendor layer in the frame even while the origin stays open.
What the May 15 Advisory Said
The May 15 warning on ShinyHunters was written for schools, not for the Hoover Building. Alert I-051526-PSA told the public that ShinyHunters specializes in large data theft and extortion, and that victims may get an email signed with the group’s name. It then described the pressure campaign the group now wants erased.
THE CHARGES THE GROUP WANTS CUT
- Exaggerated access: The warning said actors often use real or inflated claims of access to sensitive or personal information to prompt payment.
- Harassment and swatting: It said ShinyHunters actors commonly send threatening texts and calls to victims and their families, and in some cases swat them, meaning a fake emergency call meant to draw a heavy police response.
- Fake compromising files: It said actors may falsely claim to hold embarrassing photographs or videos of victims, which frequently do not exist.
- The money line: Among the steps for anyone contacted, the bureau wrote, “Do not send payment or respond to their demands.”
ShinyHunters answered those lines one by one. It said its threats “are very real,” that it has never swatted corporate victims’ staff or texted their families, and that it has never claimed to hold embarrassing photos or videos. In capital letters it added that it is not a sextortion crew and is not part of “The Com,” a label it called industry propaganda.
The May warning never used the word sextortion. The group read the line about compromising photos that way anyway. It is also asking the FBI to withdraw a document whose first practical instruction to the public was not to pay, after a spring in which a major education vendor did reach an agreement with the same crew.
Oracle’s PeopleSoft Bug Did Not Stay Theoretical
ShinyHunters told reporters it found a new PeopleSoft zero-day on the night of September 21 and used it at once against an FBI server tied to recruiting. It described remote code execution, then lateral movement. One screenshot it shared showed a page on apply.fbijobs.gov under a /PSEMHUB/ path, the Environment Management Hub used in PeopleSoft.
That product family was already a live problem. On June 10, Oracle published a security alert for CVE-2026-35273, a bug it said allowed unauthenticated PeopleTools remote code execution. The score was 9.8 out of 10. Google’s Mandiant unit said the same crew had been exploiting the flaw from May 27 through June 9, hitting about 100 organizations across about 300 instances, most of them U.S. schools.
Oracle’s own matrix lists the flaw in the Updates Environment Management component on PeopleTools versions 8.61 and 8.62, reachable over HTTP with no login. A later June patch bundle folded in fixes for that alert. Whether the FBI jobs stack was unpatched from that wave, or whether the group found a second PeopleSoft flaw as it now claims, is exactly what the bureau says it has not settled.
THE SAME PRODUCT, TWO SEASONS
| Item | June PeopleSoft campaign | September FBI jobs claim |
|---|---|---|
| When | Mandiant saw exploitation May 27 to June 9 | Group says it got in on September 21 |
| Software named | PeopleSoft PeopleTools 8.61 and 8.62, CVE-2026-35273 | Group says a PeopleSoft remote-code flaw, no CVE issued for a new bug |
| What officials confirmed | Oracle alert on June 10; Google notified more than 100 potentially exposed orgs | FBI confirms a probe of FBIJobs.gov claims, not the path or the haul |
| Demand | Classic steal-and-leak pressure, including universities | Retract or remove the May 15 warning within one week |
| Scale claimed | About 100 organizations, about 300 instances | 2 to 3 terabytes on almost all agents plus applicants |
A jobs portal on PeopleSoft is still an HR system that stores names, contact files, and application packets. If the group also reached the Criminal Justice, HR, and Medlink services it listed, the blast radius grows. Those names remain the group’s labels. The FBI has not adopted them.
A Spreadsheet of Names, Assignments and Home Addresses
ShinyHunters says the stolen store is 2 to 3 terabytes and covers “almost ALL FBI Agents and individuals who filed an application with the FBI for a job,” in any role. It has not posted the full dump. It did pass around a sample of about 5,000 rows.
Reporters who saw that sheet described names, home addresses, phone numbers, dates of birth, Social Security numbers, emergency contacts, spouses, some medical fields, and job assignments. Some phone numbers and names matched real staff. Assignment text in the sample pointed to work on Chinese spies, Russian intelligence, and drug cartels, which is the kind of line that makes a home address more than an identity-theft problem.
Office of Personnel Management counts compiled by USAFacts put 34,867 FBI employees as of May. “Almost all” of that workforce, plus a pipeline of applicants, is a claim, not a confirmed inventory. A 5,000-row sample can prove that some real people are in the file. It cannot prove the rest.
WHAT IS ON THE RECORD
- The claim: Sensitive data on almost all FBI agents and on people who applied, taken after a PeopleSoft break-in.
- The sample: About 5,000 rows with home contact fields and, in some lines, duty descriptions.
- The match work: Some identities in the sample lined up with real employees; the full 2 to 3 terabytes is unverified.
- The bureau’s line: It is investigating alleged impact to employee personal information and has not named a volume.
Joseph Cox, the reporter who first described the sample, put the intelligence problem in a short note.
This data presents significant national security and counterintelligence risks, and isn’t in the hands of a foreign intelligence agency, but a group of likely younger, English-speaking hackers.
Joseph Cox, reporter, in an email
A security analyst who asked not to be named, to avoid retaliation, said the bureau’s counterespionage and counterterrorism missions make that file dangerous in a different way. It could wreck an employee’s ability to work undercover or travel, and it can be used against families. On the group’s claim that this is not extortion, the same analyst said, “Never trust anything they say. Ever.”
Personnel files from a hiring system are not the bureau’s classified case files. Nothing public shows ShinyHunters reached wiretap platforms or investigative databases. Home addresses, spouses, and a line about who works China or cartels are still enough to harass, swat, or out a person who was supposed to stay hard to find.
FBI Applicants Carry the Same Personal Risk
The leak-site post puts applicants in the same sentence as agents. That is easy to skip if the story is framed only as a raid on current staff. It should not be skipped. A person who filled out an FBI packet handed over the story of their life to a site designed to receive it, and many of those people never got a badge.
Application files can hold education history, work history, references, family names, and the kind of personal detail a background check eats. Rejected candidates, people still in the pipeline, and staff who only ever used the portal to apply are all in the same pot if the group’s “filed an application” line is real. Foreign services do not need those people to be current agents. They need a list of who wanted in, who got close, and who can be pressured.
The group says it is not selling the file. Motive does not move the copy. Once a recruiting dump exists on a leak site’s side of the wire, it can be stolen again, seized in an arrest, or handed to someone who will pay. Kaiser’s point about a target on their back cuts both ways. It raises the odds of a federal case, and it raises the odds that someone else eventually holds the same sheet.
This is also a bad week to learn that the public face of FBI hiring still sat on a product ShinyHunters had already used, in June, to walk into about 100 other organizations. Schools were 68 percent of the victims Google warned. The FBI’s portal was supposed to be a different class of system. On the group’s account, it was not.
Seven Days to Retract a Warning
The May education breach is the reason the warning exists. ShinyHunters claimed data tied to nearly 9,000 schools on the Canvas platform, defaced login pages, and pressed Instructure, the vendor, through a mid-May deadline. Instructure later said it reached an agreement with the “unauthorized actor,” that data was returned, and that it received digital confirmation of destruction, with an assurance that customers would not be extorted.
The FBI’s May 15 notice still told the public not to pay. Four months after that notice, the same crew is using the FBI’s own hiring site as a lever to get the notice taken down, and it is using the same “next headline” close it has used on companies.
FROM THE SCHOOLS WARNING TO THE JOBS PORTAL
- May 15, 2026: The FBI issues PSA I-051526-PSA on ShinyHunters after the learning-platform attack and tells people not to pay.
- May 27, 2026: Mandiant later dates the start of PeopleSoft exploitation by the same group around this day.
- June 10, 2026: Oracle publishes the CVE-2026-35273 security alert for unauthenticated remote code execution in PeopleTools.
- September 21, 2026: ShinyHunters says it found a PeopleSoft flaw that night and used it on an FBI recruiting server.
- September 22, 2026: Apply.fbijobs.gov is defaced; the group posts that it holds data on almost all agents and applicants and starts a one-week clock.
- September 23, 2026: The FBI says it is investigating alleged impact to employee personal information and that the point of breach is still undetermined.
- September 29, 2026: The week the group granted for a correction or removal of the May warning runs out.
The group’s one-week clock runs to September 29. The FBI has not said whether it will alter the May 15 warning, and it has not confirmed how much staff data left the jobs system.

Kering’s Growing Houses Cannot Outrun a Shrinking Gucci

Studio Staff and Bitcoin Buyers Built the Eminem Leak Case

A Mutated H1N1 Strain Is Hitting Younger Immunity First

Albert Heijn Returns at One-Third as Rivals Take Share

Art Basel Paris Ends After One Public Day

Thameslink Will Pad 60,000 Ironing-Board Seats From 2027

How Tall Was Adolf Hitler Really? Debunking the Myth of his Height

Micron Sells the Memory Shortage as Five-Year Contracts

Royal Caribbean Sends Los Angeles Ships to Singapore and Brisbane

U.S. Forces Clear Hormuz Mines, Then Hit Minelayers Again
-
 NEWS2 months ago
Thameslink Will Pad 60,000 Ironing-Board Seats From 2027
-
 SCIENCE3 years ago
How Tall Was Adolf Hitler Really? Debunking the Myth of his Height
-
 NEWS2 months ago
Micron Sells the Memory Shortage as Five-Year Contracts
-
 NEWS2 months ago
Royal Caribbean Sends Los Angeles Ships to Singapore and Brisbane
-
 BUSINESS2 months ago
U.S. Forces Clear Hormuz Mines, Then Hit Minelayers Again
-
 BUSINESS2 months ago
Sweetmore Bakeries Buys Fantasy Baking for Bar Work
-
 BUSINESS2 months ago
L Catterton Installs a Kraft Heinz Operator at Kettle Cuisine
-
 NEWS2 months ago
CISA’s 100 Water System Hacks Hit One-Operator Plants